And don’t you dare use stuff like
,orças a special character!I like it when they ban ;
if they ban ; i’m using &. fuck yo database.
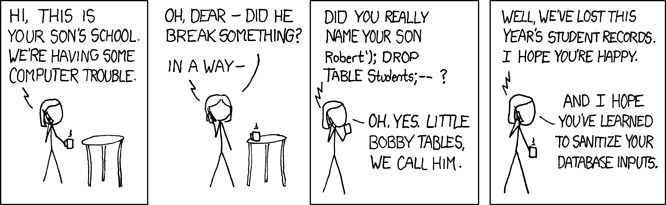
Sanitize yo shit mf, that’s not my problem.
In systems that accept whitespace, “Live, Laugh, Love” is considered a strong password.
With that being said, “In systems that accept whitespace, “Live, Laugh, Love” is considered a strong password.” is an even stronger password.
I love systems that accept “With that being said, “In systems that accept whitespace, “Live, Laugh, Love” is considered a strong password.” is an even stronger password.” as my password.
For those that have full Unicode support, including newline characters and a very high or nonexistent character limit, using:
For those that have full Unicode support, including newline characters and a very high or nonexistent character limit, using:
I love systems that accept “With that being said, “In systems that accept whitespace, “Live, Laugh, Love” is considered a strong password.” is an even stronger password.” as my password.
as your password is an even stronger password.
as your password is an even stronger password.
all fun and games until you find out it strips whitespace/newlines on save without telling you and you gotta go figure out why your passwords not working
This reads like xkcd
That is a wonderful compliment. Thank you.
It’s also a gigantic red flag when sites say there’s a password limit
Bitch, my password is supposed to be hashed so even if I uploaded the LOTR trilogy extended edition in 4K, it should still come out the same length as any other SHA256 hash
I make my passwords complex phrases with spaces and punctuation included. e.g. “Correct, horse battery staple!”
(obligatory that’s not my password)
Yeah, no way someone can brute force that
If you mean that as sarcasm, there are multiple calculations of the complexity of such a password, in which it performs no worse than a random password of a typical length. Although for myself I still prefer random passwords stored in a password manager, with extra special characters and quite some reserve in length.
Nah, it was not sarcasm, i’d use them myself if i wasn’t lazy, i just make my password manager generate and store the password
I appreciate the enthusiasm but my load balancer will get sad if I let you send more than 1500 bytes.
First round of hashing could be done client-side, and then send that to the server.
Would be cool to also add salt so that the hash couldn’t get re-used across services even with the same source password/file if somehow captured.Idea:
- Enter username
- Server sends salt to client
- Enter password or key file
- Client computes hash of the password or file with salt added (I have no idea how it’s used. If appended, some hashing functions could truncate the data, losing the salt. If prepended along with truncation, you just made the password even shorter. XOR?)
- Client sends hash to server
- Server hashes the hash same way as if it was password
- If it matches, you’re in
Basically, the hash is your password. Data can be whatever.
Most websites already use JavaScript, so why not.So, I was having trouble sleeping last night and found myself mulling over your idea.
As any good sleep deprived tech I went down a rabbit hole. There are solutions that prepare the encrypted payload on the client side. But, why you don’t see solutions offering you to authenticate with the entire lotr series is that you hit a ceiling really fast where more data is the same security threshold as the former smaller data.
If you want to derive security from large data there’s already a scalable solution in the form of private public key pairs, where the size of the key is directly tied to the security. So if you convert lotr to a prime number you can get somewhere with that approach.
I’ve thought of the point where password length becomes irrelevant as well. Unless there some maths I don’t know that plays a role here, longer passwords become useless when x^n > K. Where x is the character set available for the password, n is the smallest length that meets the criteria of the formula, and K is the hash functions key space. Effectively, this would be due to the fact that brute forcing would be just as likely to find a collision as it would the actual password used.
Basically, the hash is your password
Exactly, this is equivalent to using a password of a particular length with only hex digits. It may be long, but the original data is completely unnecessary here.
The salt adds nothing
It prevents cross-service re-use, should the original password hash be obtained (if other services used the same system).
Example (MD5 in b64 used for simplicity): Same password is used on website1 and website2. The password is
password.
passwordproducesKGdV+tBIacpSMyCszg3GpA==which can be used for both websites.
Now, if website1 addssbo2as salt, and website2 addsx3e5, you get:
passwordsbo2->d0bd511zpYqG3//3vLGYRQ==
passwordx3e5->788BnQKx7B2KOSju2jviiQ==So if you are on a corporate network that does MITM (you had to add their root cert) for monitoring, they’ll only see a hash for each website separately, without being able to re-use it.
Though that’s quite a bit of an edge case, and assumes no client modification or other monitoring.True, I got engrossed in thinking through your proposal and forgotten about the original intent of a salt. Happens to me from time to time, particularly with security topics for some reason.
I’d rather not make the client do anything like that, you cannot trust a client, EVER; what if some script kiddie tries to send the clear passwd by modifyng the request? Ofc it’s a very minor problem but still…
You already trust the client with your password regardless.
I wouldn’t send the salt to the client. Have it hash the password, then the server hashes that with the salt for comparison and storage.
But that would mean you can’t verify the password complexity server side, which can be bad for certain accounts.If there would be an advantage to doing so, the server could still do that anyway. You’d just end up storing client salt and server salt.
My main concern was MITM which doesn’t modify the webpage if web UI is used, such as on corporate networks which require client devices to have that network’s root certificate for scanning and activity logging.The client salt would need to be consistent and “public” since the client needs it before login. It’s basically useless.
You could write a browser extension that converts your password to a hash. You could pick the hash yourself so the server has no way to figure what the original password was.
You would essentially achieve the same thing.
Clearly you have undiscovered SHA256 collisions that you want to attack the website with.
You shouldn’t be using SHA256 to hash passwords though.
Must be 8 to 14 characters 😡
alphanumeric characters only, and maybe an underscore if we’re feeling extra generous
correct horse battery staple
Fun fact: As an anti-scam measure, if you type your password in a comment, Lemmy will automatically censor it for you.
Like this:
************
Cool, right?
11 year old me fell for this on runescape
How does mine look?
Hunter2
I just see *'s.
Really the same weak ass jokes from reddit huh?
This joke has been circulating around since the IRC days.
This joke is older than Reddit, youngling.
I felt like a celebrity when my old IRC handle popped up on bash.org for one line. I didn’t even say anything funny, just the “what?” that set up someone else’s joke, but it was cool to see me there.
The internet was so much better when it was just, like, ten people.
Reddit? My boy, this meme predates reddit.
It’s a bash.org original. Unfortunately no longer online, but you can visit bash.rip now with the same quotes
This is just a css trick. Your full password text is still there in the html.
hunter2 x Hunter2
When you paste my password I can still see it!
But in all honesty, poor Hunter2 is probably getting scammed for his Social Security benefits by now 🥲
Calm down, Satan.
Let me introduce you to MyP4s$worcl*websitename**@
The new recommendation is 30 character or more passphrases with some noise.
My last job was at AutoZone and our password requirements were stricter and had to be changed twice as often as my password on our secured computer when I was in the Navy.
You never know when them O’reily boys will try and hack you. You gotta be prepared!
for real, why is it so hard to count entropy?
I guess it’s too chaotic.
The FBI training I’m forced to take at work suggests replacing characters in that manner. “Just use a $ instead of S!”
But back in like 2006 I brute forced a dump of 20 Windows passwords in that style on my old Dell single core machine in less than two seconds. Every passing year I’m still shocked people still think this is secure.
My new job has us doing various security trainings every month and they also send out fake phishing emails. I initially ignored the emails prompting me to do the training because they require you to click a personalized link in the email to access the training. Eventually, my manager reached out and asked why I hadn’t done the training, so I explained, but finally clicked through to do it. That month’s training was about how a long passphrase is more secure than a list of character type requirements. Guess whose password requirements are a list of character type requirements?
Requiring specific characters reduces the number of permutations. The only thing that makes a password more secure is increasing the minimum length. As the OP suggests, enforcing special characters makes most people just put a special character at the end. What you have effectively done is make the last character so easy to guess that it might as well not exist.
Your password must be at least 10 characters long.
ERROR: INVALID PASSWORD ENTERED!!!
PASSWORD MUST NOT EXCEED 12 CHARACTERS!
Even better when it doesn’t tell you and just drops the last characters.
Do you want your password to be sent raw into a service to analyze your password entropy and detect common patterns, OR do you want a simple rule which can be checked client side?
Analyze password entropy client-side. https://dropbox.tech/security/zxcvbn-realistic-password-strength-estimation
You don’t send full raw hashes, k-anonymity is a thing. HaveIBeenPwned just takes the first 5 of a hash and sends you back a list that you compare clientside so it never leaves as a usable password.
Lemmy devs still haven’t figured this out.