

They did similar things to block the pirate bay, I guess 💀
There’s an important follow-up post. https://lina.sh/blog/cuii-gives-up
The Clearingstelle Urheberrecht im Internet (CUII) is a private group formed by ISPs and copyright holders. They decided what websites to block, and ISPs followed, without any court ruling. No judge was involved, no legal process.
The members: The four largest ISPs in Germany and a bunch of copyright holders (the Motion Picture Association, Sky, …). If they decided that a site should be blocked, the ISPs just blocked the domains from being resolved. This ran completely outside the courts, a private system made by corporations for censorship. Blocked sites included streaming services, but also sites like Sci-Hub or game piracy sites.
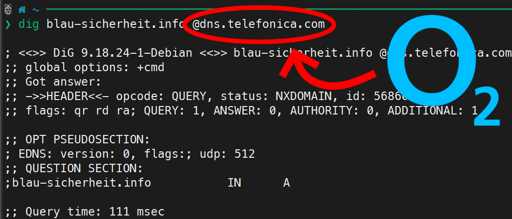
In a previous blog post, I went into detail on how we trolled them:
- We leaked their secret blocklists (the list of domains was kept secret!)
- We exposed dozens of wrongful and outdated blocks.
- We made them unblock a lot of domains, including some that were blocked for years.
- … and so much more. We just made a lot of bad press for them.
The CUII now only coordinates blocks between ISPs after a court order. That’s it. No more secret votes. No more corporate censorship. The new version of their website says: “The CUII coordinates the conduct of judicial blocking proceedings and the implementation of judicial blocking orders.”
…
In Germany, we have the Clearingstelle Urheberrecht im Internet (CUII) - literally ‘Copyright Clearinghouse for the Internet’, a private organization that decides what websites to block, corporate interests rewriting our free internet. No judges, no transparency, just a bunch of ISPs and major copyright holders deciding what your eyes can see.
This is worse than whatever the UK is doing IMO.
Recently they switched to a more public court-order based approach.
But my thought on this is as well: Once their domain name servers are configured according to law, can they force us to not use other domain name services?
They probably can just block IPs of foreign DNS but I suspect there’s ways of mirroring around that.
There is DoT, DoH and oblivious dns techniques. The problem is - users will have to configure those and aint nobody got time for that.
Theoretically an ISP can block all outgoing queries to the DNS port 53 except to whitelisted servers, but now DNS over HTTPS exists, haven’t looked into how blockable that one is.
At this point you can copy Chinas great firewall I guess.